
Cloud-based integrated network and security service
Cloud-based integrated network and security service
Overview
SASE integrates network connectivity and security functions into a single platform, providing an environment where branch offices, data centers, cloud, and remote users can securely and quickly access internal applications.
Optimize network routes and apply various security functions with consistent policies, regardless of internal or external distinctions. Additionally, a single-platform dashboard enables integrated monitoring and management of network and security across all segments.
Architecture Diagram
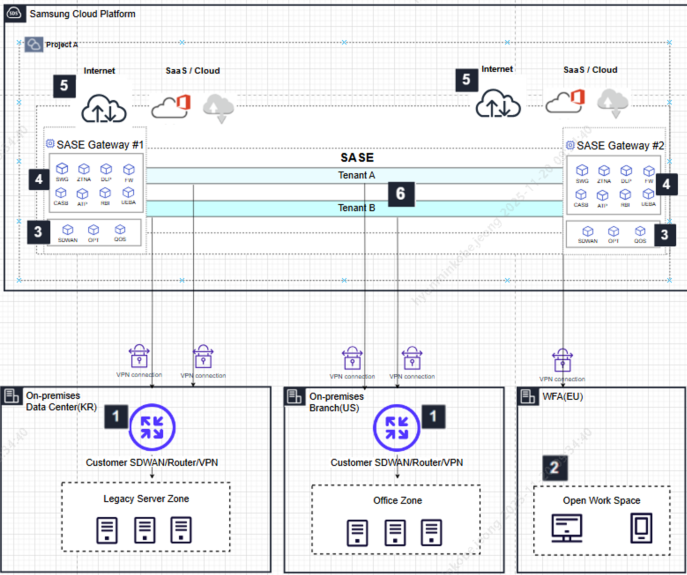
Configure the SASE Last-Mile environment for the customer’s data center and site.
- We request the installation of physical equipment (router, SD-WAN, etc.) required for Customer Edge and line management.
- After requesting the provisioning of lines such as Internet, dedicated lines, and MPLS, connect via IPsec.
Mobile devices install the provided Agent or connect via an Agentless VPN.
Apply the network functions of the SASE Gateway selectively as needed.
- SD-WAN
- QoS
- Optimization
Apply the security features of the SASE Gateway selectively as needed.
- SWG
- FW
- DLP
- CASB
- ZTNA
In addition to the site’s local internet, a separate internet connection is provided from the SASE PoP.
Provides additional communication services to sites, data centers, and mobile users across regions through the SASE network.
Use Cases
A. ## Zero Trust remote access for remote and hybrid workers
Users can access corporate applications anytime, anywhere through the SASE Agent or browser-based ZTNA.
Grant minimal permission access based on the user’s ID, device status, and location. This enables the same level of security and user experience regardless of location, without the need for separate VPN equipment.
B. ## Multi-cloud·SaaS traffic integration security
Traffic destined for AWS, Azure, GCP, and major SaaS (Microsoft 365, Salesforce, etc.) is aggregated to the SASE cloud.
By applying SWG, CASB, and DLP policies uniformly, you can prevent data leakage and comply with security regulations without having to deploy separate security appliances for each cloud.
C. ## Global Branch WAN Optimization
Connect worldwide sites with an internet-based SD‑WAN and provide regional local breakout through SASE PoPs.
By applying acceleration, QoS, and SD‑WAN policies at PoPs adjacent to the traffic, we reduce the cost of traditional leased lines while delivering a consistent level of network quality.
Prerequisites
None
Constraints
None
Considerations
None